


UFO hackers infiltrated high-security government networks between 1992 and 2002, driven by a singular mission: to uncover suppressed information about extraterrestrial contact. These cyber intruders, Quenton, Gary McKinnon, and Matthew Bevan, claimed to have discovered evidence of secret space programs and non-terrestrial personnel during their unauthorized access to military systems. Their actions not only fueled conspiracy theories but also catalyzed significant reforms in cybersecurity protocols that continue to influence digital defense strategies today.
The Anonymous Pioneer: Quenton (1992)
In 1992, the world got its first glimpse of government system vulnerability when a mysterious figure using the alias “Quenton” appeared on NBC’s Dateline. With his identity concealed through voice alteration and face obscuration, Quenton claimed to have successfully breached classified networks at Kirtland and Wright Patterson Air Force Bases, locations long rumored to house UFO research facilities.1
Despite extensive investigation by UFO researcher T. Scott Crane, Quenton’s true identity remains unknown to this day. However, his televised claims sparked public interest in government secrecy surrounding extraterrestrial phenomena and inspired future hackers to pursue similar digital explorations.
Gary McKinnon: “The Biggest Military Hack of All Time” (2001)
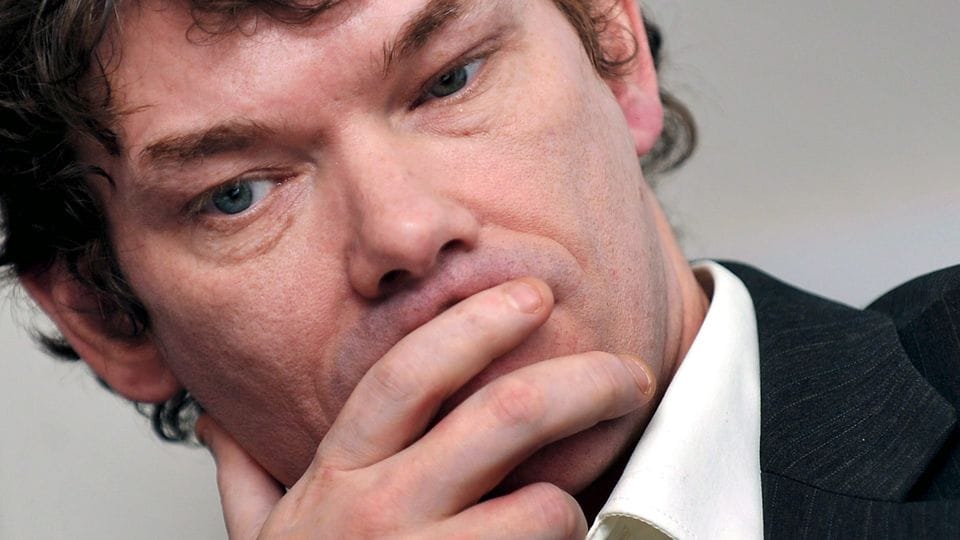
British citizen Gary McKinnon executed what U.S. prosecutors would later call “the biggest military computer hack of all time” during a 13-month cyber campaign targeting NASA and Department of Defense systems. Motivated by disclosures from Steven Greer’s Disclosure Project, McKinnon sought evidence of free energy technology and extraterrestrial contact that he believed governments were concealing from the public.2
McKinnon’s hacking techniques were surprisingly simple, he exploited weak security practices, including default passwords like “administrator” and “password” that had never been changed on critical systems. Despite these basic methods, his discoveries were extraordinary, according to his claims:
- A high-resolution image of a UFO stored on computers at NASA’s Johnson Space Center
- Spreadsheets titled “Non-Terrestrial Officers” and “Fleet-to-Fleet Transfers” containing names not found in conventional naval records
- Evidence of technology suppression related to alternative energy sources
The legal aftermath of McKinnon’s activities was equally remarkable. Facing extradition to the United States and potential imprisonment for up to 70 years, McKinnon engaged in a 12-year legal battle that concluded when UK Home Secretary Theresa May blocked his extradition based on his Asperger’s syndrome diagnosis and suicide risk assessment.3 Today, McKinnon operates an SEO business but remains unable to travel outside the United Kingdom.
Matthew Bevan: The Wright Patterson Intruder (1994)
Two years after Quenton’s television appearance, Matthew “Coogi” Bevan launched his own cyber operation targeting Wright Patterson Air Force Base. Using only a Commodore Amiga 500 computer, Bevan claimed to have accessed classified information about anti-gravity propulsion systems, technology that would revolutionize aerospace engineering if proven authentic.4

Bevan’s activities were connected to those of his protégé, Richard “Datastream Cowboy” Price, who separately breached systems at Rome Air Force Base. When authorities arrested Price, the investigation eventually led to Bevan as well. However, unlike modern cybercrime prosecutions, both individuals faced minimal legal consequences when U.S. officials declined to disclose sensitive security information during court proceedings.
Impact on Cybersecurity Evolution
The government system breaches executed by these UFO hackers exposed critical vulnerabilities in military and intelligence networks that prompted comprehensive security reforms. Following these incidents, federal agencies implemented:
- Enhanced protection against Advanced Persistent Threats (APTs)
- Expanded bug bounty programs to identify vulnerabilities before malicious actors could exploit them
- Sophisticated encryption protocols for sensitive data
- Improved access controls and authentication requirements
These cyber intrusions highlighted that even the most sensitive government information remained vulnerable to determined individuals with modest technical resources. The subsequent security improvements established foundations for modern cybersecurity practices that protect both public and private sector networks today.
Digital Security Lessons from the UFO Hackers
The techniques employed by Quenton, McKinnon, and Bevan may seem primitive by today’s standards, but they exposed fundamental weaknesses that continue to plague information systems. Organizations can learn several critical lessons from these historical breaches:
- Implement robust authentication: Two-factor authentication using authentication apps provides stronger protection than password-only systems.
- Utilize strong passphrases: Complex, unique passwords significantly increase security posture.
- Deploy password management solutions: Password managers prevent credential reuse across multiple platforms.
- Enhance phishing awareness: Train users to identify spoofed emails, typo-squatted domains, and malicious links.
- Consider passwordless technologies: Biometric systems offer enhanced security through cryptographic keys.
The Enduring UFO Mystery
While these hackers claimed extraordinary discoveries, concrete evidence of extraterrestrial information remains elusive. Even NSA whistleblower Edward Snowden, who had extensive access to classified systems, stated he found no evidence of UFO-related programs during his time working with intelligence agencies.5 This absence of confirmation suggests that if such information exists, it may be compartmentalized beyond the reach of even sophisticated cyber intrusion techniques.
Conclusion
The stories of UFO hackers represent a fascinating intersection of cybersecurity history, conspiracy theory, and the human quest for hidden knowledge. Their motivations, uncovering suppressed information about extraterrestrial contact, led to actions that exposed serious vulnerabilities in government systems and ultimately strengthened digital security practices worldwide.
As we continue to debate the existence of extraterrestrial evidence in government archives, the legacy of these cyber intruders reminds us that the pursuit of hidden information can drive technological innovation and security improvements with far-reaching implications for information protection strategies.
References
Footnotes
- NBC Dateline. (1992). Interview with anonymous hacker “Quenton” regarding government UFO files. ↩
- McKinnon, G. (2006). Interview with The Guardian regarding his motivations and findings during government system breaches. ↩
- UK Home Office. (2012). Decision statement regarding Gary McKinnon’s extradition case. ↩
- Bevan, M. (1996). Court testimony regarding access to Wright Patterson Air Force Base systems. ↩
- Snowden, E. (2019). Interview with Joe Rogan Experience podcast regarding classified information and UFO evidence. ↩